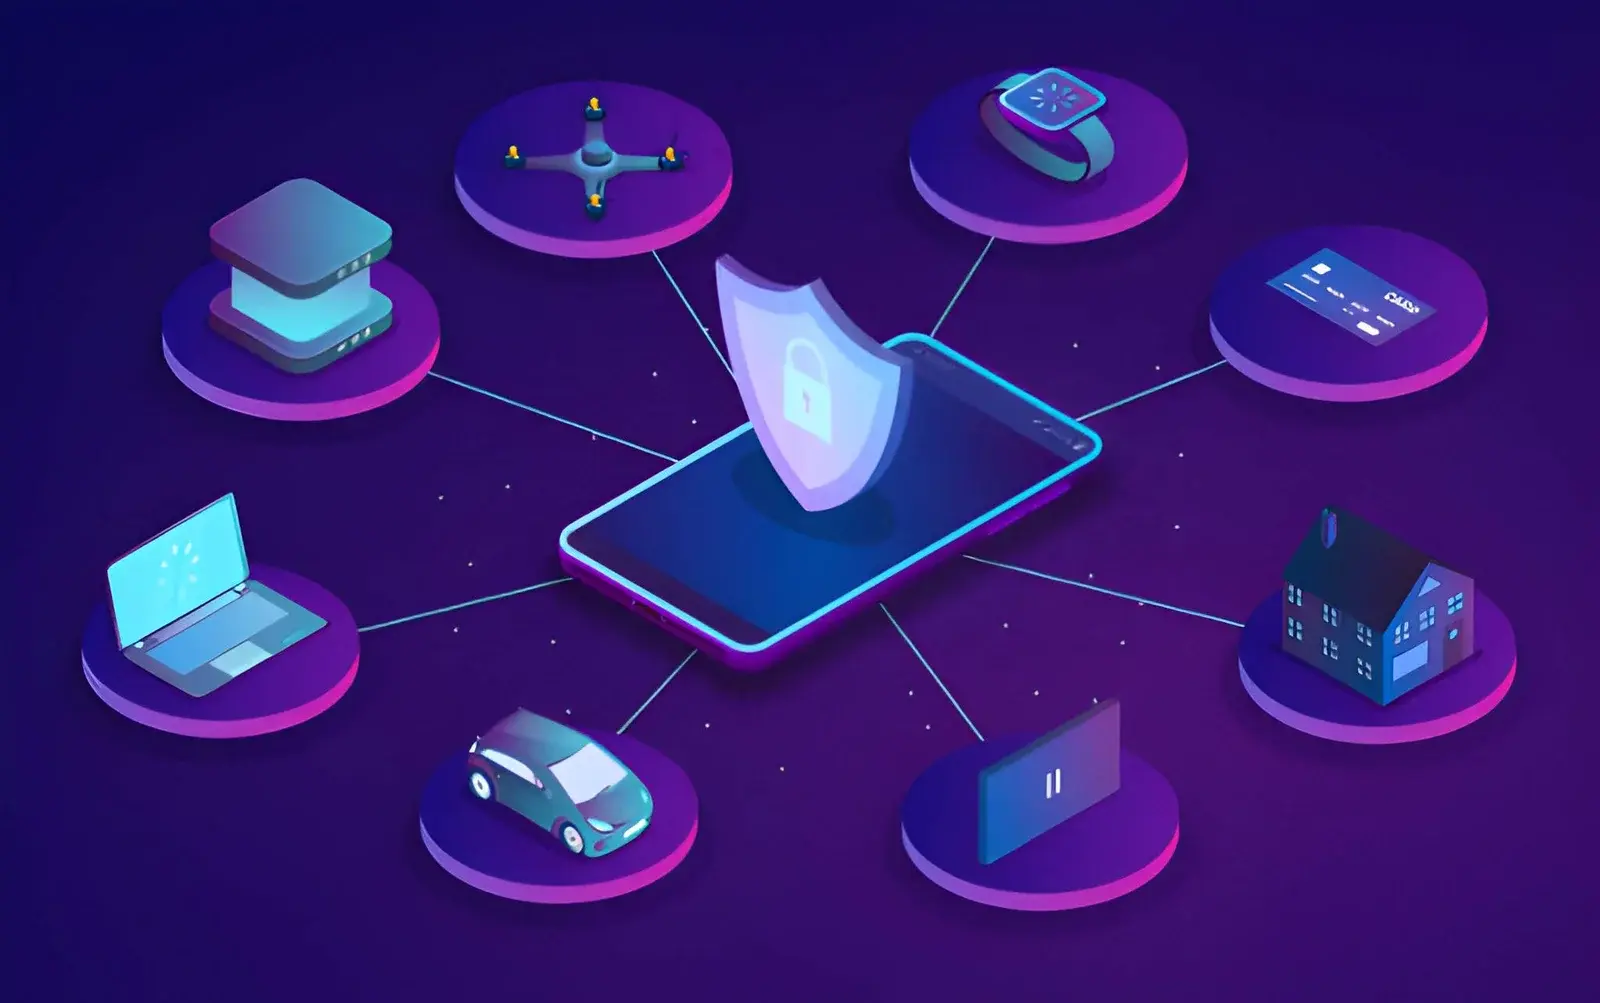

A single malicious app can expose personal information, compromise login credentials, or create a pathway into an organisation’s wider digital environment. As mobile devices become essential for banking, communication, shopping, and business operations, protecting them requires more than basic antivirus software. Businesses must also consider application vulnerabilities, suspicious device behaviour, and attacks that exploit weaknesses while apps are running.
Modern mobile threat defense helps organisations identify suspicious activity, assess application risks, and strengthen protection across mobile environments. By combining intelligent monitoring, application security, device risk assessment, and timely threat response, businesses can detect potential threats earlier and respond more effectively. A coordinated approach helps reduce digital exposure while supporting legitimate users and maintaining convenient mobile experiences.
Intelligent Protection Strengthening Mobile Security
Mobile security requires continuous visibility into applications, devices, network connections, and user activity to identify risks before they escalate.
1. Detecting Malicious Applications Before Damage Occurs
Mobile applications can introduce risks through malicious code, excessive permissions, insecure components, or compromised updates. Security teams need ways to identify suspicious application behaviour before it exposes sensitive information or affects connected systems.
- Inspect application behaviour: Identify suspicious activities, unexpected permissions, and potentially harmful processes.
- Assess application integrity: Detect signs of tampering or unauthorised modification.
- Reduce exposure: Investigate risky applications before they access sensitive business resources.
Early detection helps organisations limit exposure while maintaining greater control over the applications employees use.
2. Identifying Device Risks Across Work Environments
Personal and corporate smartphones often access email, customer records, internal applications, and cloud platforms. A compromised or poorly configured device can therefore create risks beyond the device itself.
- Check device compliance: Identify outdated operating systems, insecure configurations, and missing security updates.
- Recognise compromised devices: Detect indicators of rooting, jailbreaking, or other security weaknesses.
- Apply access restrictions: Limit sensitive access when devices fail established security requirements.
These checks help security teams make informed decisions about device access and reduce opportunities for compromised endpoints to expose organisational information.
3. Preventing Credential Theft And Account Misuse
Stolen credentials can allow attackers to impersonate legitimate users and access protected resources. Mobile phishing, fake login screens, malicious links, and unsafe authentication flows can make credential theft particularly difficult to detect.
- Identify suspicious links: Detect potentially dangerous destinations encountered through mobile applications or messages.
- Strengthen authentication: Combine secure login mechanisms with multi-factor verification.
- Monitor unusual access: Investigate unexpected login patterns and potentially compromised accounts.
Combining identity controls with mobile risk signals helps organisations reduce unauthorised access and protect important digital services.
4. Securing Mobile Connections And Network Traffic
Mobile users frequently connect through public Wi-Fi, home networks, cellular connections, and unfamiliar hotspots. Unsafe connections or interception attempts can expose information transmitted between devices and digital services.
- Assess connection risks: Identify suspicious network conditions and potentially unsafe communication paths.
- Protect sensitive traffic: Use encryption and secure communication protocols wherever appropriate.
- Restrict risky access: Apply policies when a connection presents unacceptable security concerns.
These measures support safer mobile access while helping organisations maintain visibility across changing network environments.
Mobile Threat Defense Supporting Application Security
Effective mobile threat defense connects device protection with application-level security, helping organisations identify weaknesses, detect suspicious behaviour, and respond to emerging risks across the mobile ecosystem.
1. Protecting Applications Against Reverse Engineering
Attackers may inspect mobile application code to discover sensitive logic, embedded secrets, or weaknesses in authentication and data handling. Code obfuscation, integrity checks, and secure development practices can make analysis more difficult. These protections should complement secure architecture rather than replace it. Sensitive credentials should never be embedded directly in application code, while important security decisions should be validated through trusted backend systems whenever appropriate.
2. Detecting Runtime Manipulation
Applications can face attacks while running on compromised devices or within manipulated environments. Runtime protection techniques can identify suspicious debugging, tampering, hooking, or unauthorised modification. Depending on the risk and application requirements, organisations can trigger alerts, restrict sensitive functionality, or terminate unsafe sessions. Security teams should test these controls carefully to minimise false positives and avoid interrupting legitimate customers who depend on reliable mobile services.
3. Protecting Sensitive Information
Mobile applications frequently process personal details, authentication tokens, payment information, and confidential business data. Developers can reduce exposure through encryption, secure storage, limited permissions, appropriate session management, and careful handling of sensitive information. Organisations should also minimise unnecessary data collection and prevent secrets from appearing in logs. Combining secure development with runtime monitoring helps address weaknesses throughout an application’s lifecycle, from initial release through ongoing maintenance.
4. Integrating Security Into Development Workflows
Security becomes more effective when developers identify weaknesses before applications reach production. Static analysis, dependency scanning, dynamic testing, and application penetration testing can reveal different classes of vulnerabilities. Integrating these activities into development pipelines helps teams detect problems earlier and verify fixes consistently. Regular testing after significant updates is also important because new features, third-party libraries, and configuration changes can introduce additional risks.
Building Resilient Mobile Security For Modern Businesses
Strong mobile protection depends on combining technical controls with sound governance, secure development, and informed user behaviour. Organisations should regularly review application permissions, device policies, authentication practices, vulnerability reports, and incident response procedures. They should also measure whether security controls reduce meaningful risks without creating unnecessary friction for employees or customers.
A practical strategy starts with understanding which mobile applications and devices access sensitive resources. Security teams can then prioritise protections according to business impact, test their effectiveness, and improve controls as threats evolve. Continuous assessment helps keep mobile security aligned with changing applications, operating systems, and business requirements.
Conclusion
Mobile security requires coordinated protection across applications, devices, identities, and runtime environments. Intelligent monitoring, secure coding, risk-based access, and reliable incident response can help organisations reduce digital exposure while supporting convenient mobile experiences. The strongest approach combines prevention with continuous detection and timely remediation.
For organisations seeking advanced application protection, Doverunner focuses on mobile application security through capabilities designed to help protect applications against tampering, reverse engineering, and runtime threats. Their service focus includes application shielding and runtime protection, helping businesses strengthen application integrity and safeguard digital services as mobile risks continue evolving.
Also Read
- responses-when-someone-says-you-owe-me/
- what-does-a-guy-mean-when-he-says-you-look-so-innocen/
- funny-ways-to-respond-when-a-girl-says-shes-seeing-someone/